Why DDoS Protection Matters for Dedicated Servers
Dedicated servers provide exceptional performance, reliability, and complete resource control. However, because they often host business-critical applications, websites, APIs, gaming platforms, and SaaS services, they are also frequent targets of Distributed Denial of Service (DDoS) attacks.
A successful DDoS attack can overwhelm your network, consume server resources, disrupt legitimate traffic, and cause significant downtime. Beyond service interruptions, organizations may face revenue loss, damaged customer trust, and long-term reputational harm.
Implementing effective DDoS protection is one of the most important steps in securing a dedicated server environment and ensuring continuous service availability.
What Is a DDoS Attack?
A Distributed Denial of Service (DDoS) attack occurs when a large number of compromised devices send excessive traffic to a target server or network.
The objective is to exhaust available resources and prevent legitimate users from accessing services.
Unlike traditional attacks that may originate from a single source, DDoS attacks use thousands or even millions of devices distributed across multiple locations.
WordPress Web Hosting
Starting From $3.99/Monthly
Common targets include:
- Websites
- Online stores
- APIs
- Gaming servers
- Financial platforms
- SaaS applications
- Hosting infrastructure
Common Types of DDoS Attacks
Volumetric Attacks
These attacks attempt to saturate available bandwidth.
Examples include:
- UDP Floods
- ICMP Floods
- Amplification Attacks
The goal is to consume network capacity before legitimate traffic can reach the server.
Protocol Attacks
Protocol-based attacks target networking equipment and server resources.
Examples include:
Cheap VPS Server
Starting From $2.99/Monthly
- SYN Floods
- TCP Connection Exhaustion
- Fragmentation Attacks
These attacks exploit weaknesses in network protocols to consume server resources.
Application Layer Attacks
Application-layer attacks target web applications and services.
Examples include:
- HTTP Floods
- HTTPS Floods
- API Abuse
- Login Request Flooding
Because they mimic legitimate user behavior, these attacks can be difficult to identify and mitigate.
What Is DDoS Protection?
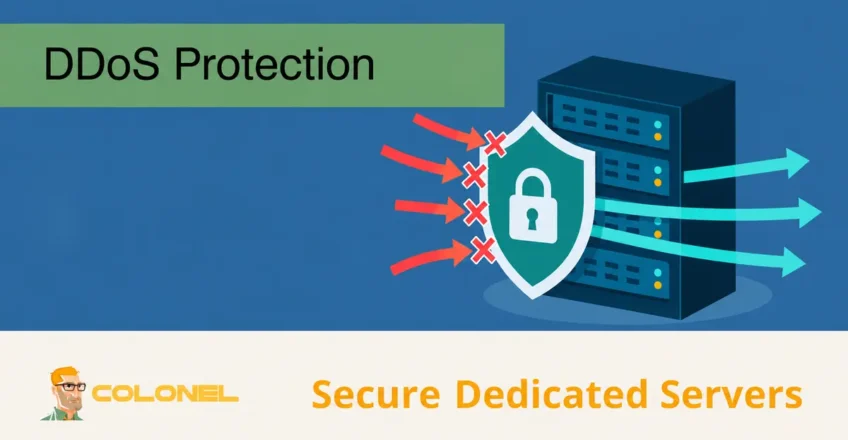
DDoS protection refers to a collection of technologies and mitigation strategies designed to detect, analyze, filter, and block malicious traffic before it impacts your server.
Modern DDoS protection solutions combine:
Windows VPS Hosting
Remote Access & Full Admin
- Traffic analysis
- Behavioral monitoring
- Packet filtering
- Threat intelligence
- Network-level mitigation
The objective is to allow legitimate visitors while preventing malicious traffic from consuming resources.
How DDoS Protection Works
Effective DDoS mitigation relies on multiple layers of defense.
Traffic Filtering
Traffic filtering examines incoming requests and identifies suspicious patterns.
The system can automatically block:
- Spoofed IP addresses
- Malformed packets
- Known attack signatures
- Suspicious connection behavior
Legitimate requests continue to reach the server normally.
Rate Limiting
Rate limiting restricts the number of requests allowed from a single source within a specific timeframe.
This technique is particularly effective against:
- Login abuse
- API attacks
- Bot traffic
- HTTP flood attacks
Traffic Scrubbing Centers
Traffic scrubbing centers are specialized infrastructures designed to process massive traffic volumes.
When an attack is detected:
- Traffic is redirected through the scrubbing network.
- Malicious traffic is removed.
- Clean traffic is forwarded to the dedicated server.
This process occurs in real time and minimizes service interruptions.
Anycast Routing
Anycast distributes traffic across multiple geographically distributed locations.
Benefits include:
- Improved redundancy
- Reduced attack impact
- Better traffic distribution
- Increased availability
Instead of overwhelming a single location, attack traffic is spread across multiple mitigation nodes.
Behavioral Analysis
Modern DDoS mitigation systems continuously analyze traffic behavior.
The system learns normal traffic patterns and can detect:
- Sudden traffic spikes
- Unusual request behavior
- Automated bot activity
- Emerging attack signatures
This allows rapid response even against previously unseen attacks.
Web Application Firewalls (WAF)
A Web Application Firewall provides additional protection at the application layer.
A WAF can block:
- Malicious HTTP requests
- SQL injection attempts
- Cross-site scripting attacks
- Bot traffic
For websites and APIs, combining a WAF with DDoS mitigation significantly improves security.
Benefits of DDoS Protection
Increased Uptime
The primary benefit is maintaining service availability during attacks.
Customers can continue accessing:
- Websites
- Applications
- APIs
- Control panels
with less disruption when attacks remain within the mitigation service’s capabilities.
Reduced Revenue Loss
Downtime directly impacts revenue for:
- Ecommerce stores
- SaaS providers
- Hosting companies
- Online services
DDoS mitigation minimizes business disruption and protects income streams.
Better User Experience
Attack traffic often causes:
- Slow page loads
- Connection timeouts
- Failed transactions
Filtering malicious traffic helps preserve performance for legitimate users; some disruption can still occur.
Enhanced Security Posture
Modern DDoS solutions often include additional security features such as:
- Firewall integration
- Threat intelligence feeds
- Traffic analytics
- Bot protection
These capabilities strengthen overall infrastructure security.
Protection of Business Reputation
Frequent outages can damage customer confidence.
Reliable DDoS protection demonstrates a commitment to service reliability and security.
Additional Security Measures
DDoS protection should be part of a broader security strategy.
Firewall Configuration
Restrict unnecessary services and ports.
Only expose services that are required for business operations.
Secure Remote Access
Protect administrative access by:
- Using SSH keys
- Disabling password authentication
- Limiting management IPs
- Enabling multi-factor authentication
Software Updates
Keep all software regularly updated:
- Operating systems
- Web servers
- Databases
- Control panels
- Applications
Security updates often address vulnerabilities that attackers may exploit.
Backup Strategy
Regular backups ensure rapid recovery if an attack leads to data corruption or service disruption.
A proper backup strategy should include:
- Daily backups
- Offsite storage
- Backup verification
- Recovery testing
Intrusion Detection Systems
IDS and IPS solutions help identify suspicious behavior before it becomes a major security incident.
Choosing the Right DDoS Protection
Confirm coverage for your actual protocols, ports and application traffic. Ask about mitigation thresholds, clean-traffic capacity, activation delays, false positives and null-routing policies. Network filtering does not automatically include a WAF or application-layer protection, and a local firewall cannot stop an attack that saturates the upstream link.
Not all DDoS protection services are equal.
When evaluating solutions, consider:
Mitigation Capacity
The provider should be capable of handling attacks significantly larger than your normal traffic volume.
Automatic Detection
Automatic mitigation reduces response time and minimizes downtime.
Layer 7 Protection
Many modern attacks target applications rather than network bandwidth.
Ensure the solution includes application-layer protection.
Global Network Presence
Large mitigation networks provide better traffic distribution and lower latency.
Monitoring and Reporting
Visibility into attack data helps improve security planning and incident response.
Who Needs DDoS Protection?
DDoS protection is especially important for:
Ecommerce Stores
Downtime directly affects revenue and customer trust.
SaaS Platforms
Service availability is critical for customer retention.
Gaming Servers
Gaming infrastructure is frequently targeted by DDoS attacks.
Hosting Providers
Service disruptions can affect hundreds or thousands of customers simultaneously.
Financial Services
Banks, payment systems, and trading platforms require continuous availability.
Enterprise Applications
Business-critical systems must remain accessible under all conditions.
Best Practices for DDoS Resilience
To maximize protection:
- Deploy network-level DDoS mitigation.
- Use a Web Application Firewall.
- Enable rate limiting.
- Monitor traffic continuously.
- Maintain regular software updates.
- Use content delivery networks where appropriate.
- Test incident response procedures.
- Maintain verified backups.
Combining these practices creates a strong defensive posture against modern DDoS threats.
Final Thoughts
DDoS attacks continue to grow in frequency, sophistication, and size. For organizations relying on dedicated servers, protection against these attacks is no longer optional. A properly protected server can withstand malicious traffic, maintain availability, and continue serving legitimate users even during active attacks.
By combining traffic filtering, scrubbing centers, Anycast routing, Web Application Firewalls, and proactive monitoring, businesses can significantly reduce risk while ensuring reliable service delivery. Investing in DDoS protection today helps safeguard revenue, customer trust, and long-term operational stability.